OwlC: Compiling Security Protocols to Verified, Secure, High-Performance Libraries
Pratap Singh
34th USENIX Security Symposium (USENIX Security '25) · Day 2 · Crypto 3: Formal Methods and Private Computation
Overview
Cryptographic protocols form the bedrock of digital security, underpinning everything from secure web traffic (TLS) to private messaging (Signal) and secure network access (WireGuard). Despite their critical importance, implementations of these protocols have been plagued by a persistent stream of vulnerabilities, some leading to catastrophic financial and data losses. While significant academic effort has focused on formally proving the cryptographic soundness of protocol designs, a substantial gap often remains between these theoretical proofs and the security of the actual code deployed in production environments. This talk addresses precisely this disparity, highlighting how even a perfectly designed protocol can be rendered insecure by flaws in its implementation.
Key moments
- 0:00 Introduction and the problem of secure protocol implementation
- 1:25 OwlC's solution: a security-preserving compiler for protocols
- 2:00 OwlC's architecture: from Owl design to verified Rust
- 2:40 Demonstrating the Owl language and explicit leakage challenge
- 4:00 Using interaction trees to specify intended I/O effects
- 5:05 Ghost linear permissions tokens enforce allowed code effects
- 6:20 Addressing implicit information leakage via side channels
OwlC: Compiling Security Protocols to Verified, Secure, High-Performance Libraries
Speakers: Pratap Singh
Conference: USENIX Security
YouTube: https://www.youtube.com/watch?v=Aay5GMluqxQ
Overview
Cryptographic protocols form the bedrock of digital security, underpinning everything from secure web traffic (TLS) to private messaging (Signal) and secure network access (WireGuard). Despite their critical importance, implementations of these protocols have been plagued by a persistent stream of vulnerabilities, some leading to catastrophic financial and data losses. While significant academic effort has focused on formally proving the cryptographic soundness of protocol designs, a substantial gap often remains between these theoretical proofs and the security of the actual code deployed in production environments. This talk addresses precisely this disparity, highlighting how even a perfectly designed protocol can be rendered insecure by flaws in its implementation.
Pratap Singh introduces OwlC, a novel security-preserving compiler designed to bridge this critical gap. OwlC takes formally verified protocol designs, expressed in the Owl language, and automatically translates them into executable Rust code that is itself formally verified to be secure. The core innovation lies in OwlC's ability to guarantee the absence of both explicit information leakages—where secret data is inadvertently written to public outputs—and implicit information leakages, which manifest as classic digital side-channel attacks through timing or memory observations.
The significance of OwlC stems from its dual promise: delivering robust security guarantees without compromising on performance or interoperability. By employing a novel mechanism for controlling "effects" within the generated code, OwlC ensures that the implementation strictly adheres to the protocol's intended behavior and nothing more. The result is high-performance, drop-in replacement libraries for complex, industrial-strength protocols, demonstrated through a compelling case study of the WireGuard VPN, achieving state-of-the-art performance while retaining formal verification.
Background
▶ Watch: Introduction and the problem of secure protocol implementation (0:00)
The digital infrastructure of the modern world relies heavily on the integrity and security of cryptographic protocols. Protocols like TLS (Transport Layer Security), WireGuard, and Signal are ubiquitous, securing sensitive communications across the internet. However, their pervasive use also makes them prime targets for adversaries. The history of these protocols is unfortunately dotted with high-impact vulnerabilities, such as various TLS bugs, which have cost organizations hundreds of millions of dollars to mitigate. These incidents underscore a fundamental challenge in cybersecurity: the disconnect between theoretical protocol design and practical implementation.
For decades, cryptographers and security researchers have developed sophisticated methods to prove the cryptographic soundness and security of protocol designs, often specified in formal documents like RFCs. These efforts ensure that, in an ideal world, the protocol logic itself is free from flaws. Yet, the persistent stream of real-world attacks reveals that a secure design does not automatically translate to a secure deployment. The problem lies in the implementation—the actual code that translates the abstract protocol specification into runnable software. A malicious or buggy compiler, or even human error during manual coding, can introduce vulnerabilities that subvert the protocol's intended security properties.
OwlC builds upon prior foundational work, specifically the Owl project, which serves as a protocol design verifier. In the Owl ecosystem, protocol designers first specify their protocols in the Owl language, a domain-specific language tailored for cryptographic protocols. The Owl verifier then checks these designs for cryptographic soundness, ensuring the high-level logic is secure. OwlC extends this pipeline by taking these already verified Owl protocol designs and compiling them into executable code. For its verification bedrock, OwlC leverages Varys, a new automated program verifier specifically developed for Rust, which plays a crucial role in formally guaranteeing the security properties of the generated implementation. This integrated approach aims to close the critical gap between formally verified protocol designs and their secure, high-performance code implementations.
Key Findings
▶ Watch: OwlC's architecture: from Owl design to verified Rust (2:00)
The central finding of this research is the successful development and demonstration of OwlC, a security-preserving compiler that effectively bridges the long-standing gap between formally verified cryptographic protocol designs and their secure, high-performance implementations. OwlC represents a significant advancement by providing an automated pipeline to generate formally verified code from abstract protocol specifications.
The compiler introduces novel mechanisms for precisely controlling "effects" in the generated code, which is fundamental to its security guarantees. Specifically, OwlC ensures that the compiled code performs exactly the operations defined by the protocol and nothing more, thereby eliminating unintended side effects that could lead to vulnerabilities. This control is achieved through two primary innovations:
- Prevention of Explicit Information Leakage: OwlC leverages interaction trees (i-trees) as a formal, first-class data structure to specify the intended input/output behavior of a protocol. To enforce that the generated code adheres strictly to this specification, it employs ghost linear permissions tokens. These unforgeable tokens, managed by the Varys verifier, represent explicit permissions to perform specific effects (like sending data over a network), ensuring that no secret information is inadvertently written to public outputs.
- Prevention of Implicit Information Leakage (Side Channels): Addressing the more subtle threat of side-channel attacks (e.g., timing or memory-based leakages), OwlC extends traditional type abstraction techniques. While type abstraction typically cloaks secret values, cryptographic protocols often require certain secret-dependent operations (like checking decryption success) that could otherwise introduce side channels. OwlC introduces a carefully controlled declassification mechanism, treating declassification itself as an effect that requires an i-tree token. Crucially, Owl's prior cryptographic analysis of the protocol guides which declassifications are cryptographically safe, preventing unchecked declassification from reintroducing vulnerabilities.
These techniques enable OwlC to generate fully interoperable, drop-in replacements for realistic, industrial-strength protocols, such as WireGuard and HPKE. Furthermore, the generated code achieves state-of-the-art performance, demonstrating that formal security guarantees do not necessitate performance compromises. The entire compilation and verification pipeline, from a checked Owl protocol to a verified Rust library, is fully automatic, making it a highly practical tool for developing secure cryptographic software.
Technical Deep Dive
▶ Watch: Demonstrating the Owl language and explicit leakage challenge (2:40)
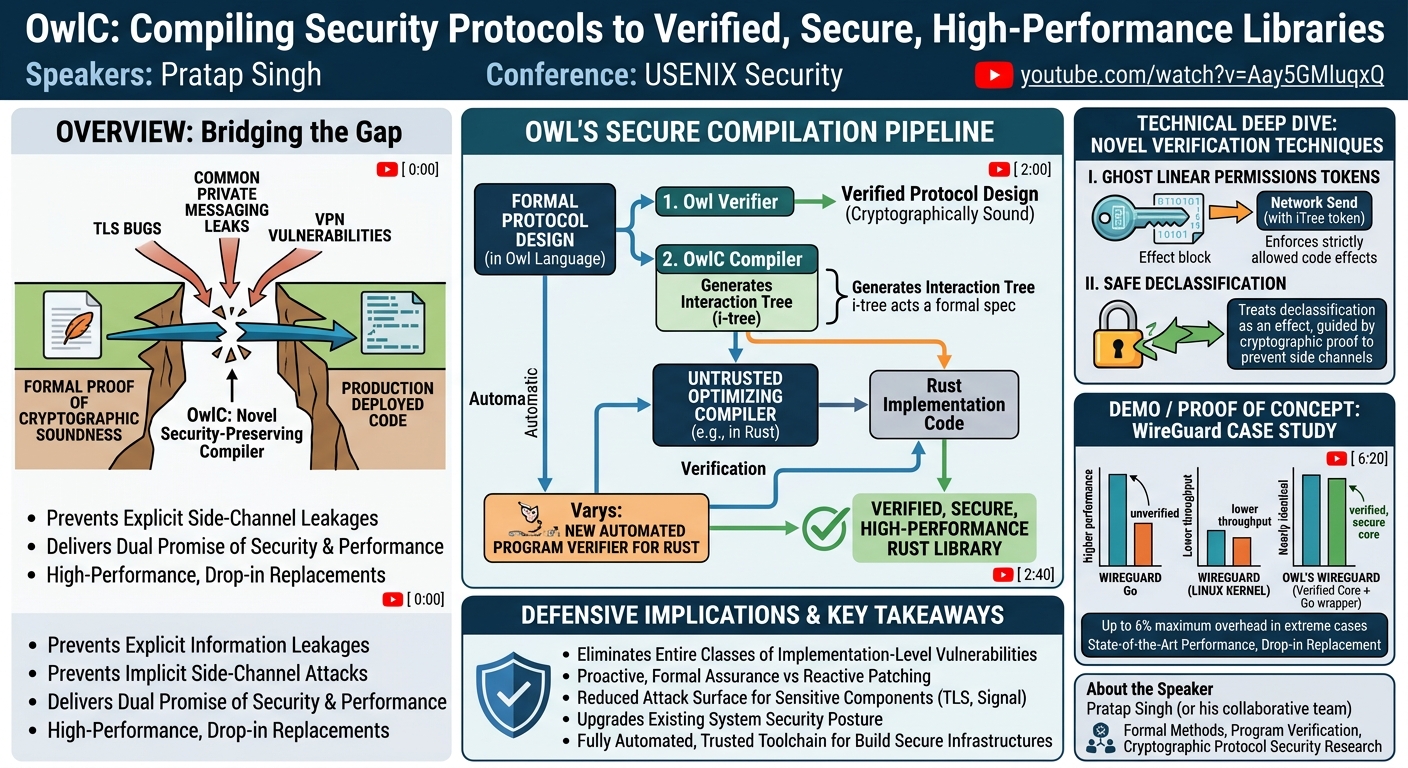
OwlC's sophisticated approach to generating secure protocol implementations hinges on a combination of formal specification, novel verification techniques, and a carefully designed compiler pipeline. The process begins with the Owl language, which serves as the source for protocol designs. As demonstrated in the talk, Owl code appears as standard pure functional code with protocol-specific extensions, allowing operations like decrypt using a pre-shared key (psk) and encrypt values. While straightforward to translate syntactically to languages like Rust, the critical challenge lies in ensuring that the generated Rust code performs only the intended operations. A naive or malicious compiler could easily insert extra input/output calls, leading to explicit information leakage—for instance, leaking a secret key kx in plaintext.
To prevent such explicit leakages, OwlC employs a two-pronged strategy:
- Interaction Trees (i-trees) as Formal Specifications: The concept of an i-tree (
iTree<A>) is borrowed from prior work and serves as a data structure to represent the behavior of programs interacting with their environment via effects. AniTreehas four constructors:
Red: Represents producing a value without effects.Input: A function that, given network bytes, dictates the subsequent computation.Output: Specifies bytes to send to the network and the continuation of the computation.Sample: Important for certain cryptographic primitives.
OwlC translates Owl protocols into i-trees through a simple one-to-one transformation, directly mirroring the control flow of the Owl code. These i-trees act as a precise, formal specification of the protocol's intended effects, which can then be reasoned about by the Varys verifier.
- Ghost Linear Permissions Tokens for Effect Control: To guarantee that the generated code only performs the effects specified by the
i-tree, OwlC introduces ghost linear permissions tokens, a novel technique developed for systems verification within Varys.
- Ghost state refers to program state that is present during verification but erased during compilation, having no runtime overhead.
- Linear state adheres to Rust's ownership and borrowing rules, meaning it cannot be created or duplicated.
Combined, a ghost linear object acts as an unforgeable permission token. In OwlC's context, a ghost linear iTree token represents the permission to perform a specific effect. For example, a network send routine doesn't just take the data to send (e.g., "hello"); it also requires an iTree token that explicitly grants permission to output "hello" and then proceed with the next steps of the protocol. By attaching such specifications to every routine that performs an effect, OwlC, verified by Varys, can formally prove that any executed effect is explicitly sanctioned by the protocol's i-tree specification.
Beyond explicit leakages, OwlC also tackles implicit information leakages, commonly known as side-channel attacks. These occur when an adversary learns secret information by observing the code's execution, such as its timing or memory access patterns. This often happens when secret information influences control flow decisions.
Traditional type abstraction techniques aim to prevent this by encapsulating secret values in opaque wrapper types, exposing only a small, safe API. However, this approach can be too coarse for cryptographic protocols, where operations like checking if decryption succeeded inherently involve secret-dependent control flow.
OwlC addresses this with a novel approach to declassification, which is the process of transforming secret information into public information. Unchecked declassification is inherently dangerous. OwlC's key insight is to treat declassification itself as an effect, requiring an iTree token. Crucially, Owl's prior cryptographic analysis of the protocol specifically identifies which values are safe to declassify and under what conditions. This allows OwlC to permit specific, cryptographically sound declassifications (e.g., revealing whether decryption succeeded without exposing the plaintext) while preventing any unchecked declassification that could lead to side channels.
The entire compiler pipeline is designed for automation and trustworthiness:
- A checked Owl protocol is first compiled into an i-tree. This
i-treeacts as the trusted specification against which all subsequent verification is performed. The simplicity of this one-to-one translation is highlighted by its implementation using a Rust macro, making the human-readable spec resemble the original Owl code. - Separately, an untrusted compiler generates a Rust implementation directly from the Owl protocol. This untrusted compiler can employ aggressive optimizations for high performance, as its correctness is not assumed.
- Finally, Varys automatically verifies that the generated Rust implementation is faithful to the
i-treespecification. This fully automatic process ensures that once a protocol is written and verified in Owl, a single command produces an interoperable, formally secure library.
Demo / Proof of Concept
▶ Watch: Ghost linear permissions tokens enforce allowed code effects (5:05)
The efficacy and practical benefits of OwlC were compellingly demonstrated through a detailed case study of WireGuard, a modern virtual private network (VPN) protocol renowned for its simplicity and strong cryptography. WireGuard is widely deployed, notably shipped in the Linux kernel, making it an ideal candidate to showcase OwlC's capabilities for real-world, high-stakes applications.
The demonstration followed the full OwlC workflow:
- The core protocol logic of WireGuard was meticulously modeled in the Owl language.
- This Owl model was then formally checked using the Owl verifier to ensure its cryptographic soundness at the design level.
- Finally, OwlC was used to generate a formally verified Rust implementation of this core protocol logic, resulting in a library of routines.
To create a fully functional WireGuard implementation, the OwlC-generated core protocol library was combined with additional components responsible for interacting with the operating system's network stack and handling multi-threading. These components were reused from WireGuard Go, which is recognized as one of the fastest open-source implementations of WireGuard. This modular approach allowed the project to leverage existing, highly optimized code for peripheral tasks while ensuring the critical cryptographic core was formally verified. The result was a complete, functional WireGuard implementation capable of serving as a drop-in replacement for the code found in the Linux kernel.
A crucial aspect of the demonstration involved performance benchmarks. The team conducted tests using a synthetic network setup, measuring the end-to-end throughput of the WireGuard tunnel under varying network delays. The results were highly encouraging:
- Baseline WireGuard Go showed excellent throughput with zero delay but became bottlenecked by network latency.
- The Linux kernel implementation of WireGuard achieved approximately two-thirds the end-to-end throughput of WireGuard Go.
- The OwlC-generated code, integrated with WireGuard Go's components, achieved performance nearly identical to the baseline WireGuard Go. It incurred a maximum overhead of just 6% under highly optimistic network latency conditions (1 millisecond). In realistic settings, OwlC's implementation performed just as well as the fastest existing implementation.
This impressive performance is attributed to OwlC's ability to generate cryptographic core operations that are as fast as their hand-optimized counterparts in the baseline. By focusing verification on the security-critical core and allowing reuse of high-performance engineering for other components, OwlC delivers both rigorous security guarantees and state-of-the-art execution speed. Beyond WireGuard, the paper details another significant case study involving HPKE (Hybrid Public Key Encryption), where similar state-of-the-art performance was also achieved.
Defensive Implications
▶ Watch: Addressing implicit information leakage via side channels (6:20)
OwlC introduces profound defensive implications for the development and deployment of cryptographic protocols, shifting the paradigm from reactive vulnerability patching to proactive, formal assurance. The most significant impact is the elimination of entire classes of implementation-level vulnerabilities that have historically plagued critical digital infrastructure. By providing formal guarantees against both explicit and implicit information leakages, OwlC directly addresses common attack vectors such as accidental plaintext logging, buffer overflows leading to secret disclosure, and subtle side-channel attacks (e.g., timing, cache, or memory access patterns) that can reveal secret keys or sensitive data.
This technology allows defenders to move beyond relying solely on extensive manual code reviews, penetration testing, and fuzzing—which are inherently incomplete and prone to human error—to a system where the security properties of the code itself are mathematically proven. For highly sensitive components like those in TLS, WireGuard, or Signal, this translates to a dramatically reduced attack surface and a much higher degree of trustworthiness. Organizations can deploy critical cryptographic libraries with confidence, knowing that the underlying implementation has been verified to adhere strictly to its security specification, performing only its intended effects and nothing more.
Furthermore, OwlC's ability to generate high-performance, interoperable code means that these enhanced security guarantees do not come at the cost of practical usability or efficiency. This is crucial for wide adoption, as performance penalties often hinder the deployment of more secure, but slower, alternatives. By providing drop-in replacements for existing, widely used protocols, OwlC facilitates a practical path for upgrading the security posture of existing systems, such as the Linux kernel's WireGuard implementation, without requiring a complete architectural overhaul or sacrificing user experience. In essence, OwlC empowers defenders by providing a robust, automated toolchain for building cryptographic software that is not just designed to be secure, but is verifiably secure at the code level, thereby significantly enhancing the overall resilience of digital systems against sophisticated attacks.
Key Takeaways
- Bridging the Gap: OwlC is a security-preserving compiler that effectively bridges the critical gap between formally verified cryptographic protocol designs and their secure, high-performance code implementations.
- Comprehensive Leakage Prevention: It guarantees the absence of both explicit information leakages (e.g., secrets written to public outputs) and implicit information leakages (e.g., timing or memory side-channel attacks) through novel verification techniques.
- Novel Effect Control Mechanisms: OwlC utilizes interaction trees (i-trees) for formal specification of effects and ghost linear permissions tokens to rigorously enforce that the generated code performs only the protocol's intended operations.
- Safe Declassification: The compiler incorporates a unique approach to declassification, treating it as an effect guided by Owl's cryptographic analysis, ensuring that necessary secret-to-public transformations are performed safely without introducing vulnerabilities.
- Automated and Performant Pipeline: The entire compilation and verification process from an Owl protocol to a verified Rust library is fully automated, producing highly performant, interoperable code, as demonstrated by the WireGuard case study (max 6% overhead compared to WireGuard Go).
- Practical Impact: OwlC enables the generation of formally secure, drop-in replacements for critical protocol components in real-world systems, offering a significant advancement in building trustworthy digital infrastructure.
About the Speaker(s)
Pratap Singh presented this work on OwlC. The transcript indicates this is "our work," suggesting a collaborative research effort. While the metadata and transcript do not specify his exact title or affiliation, the nature of the presentation at USENIX Security, a premier academic security conference, implies that Pratap Singh is a researcher or developer actively engaged in formal methods, program verification, and cryptographic protocol security. His presentation demonstrates a deep understanding of the challenges in securing cryptographic implementations and the innovative solutions to address them.
Reviews
Dr. Zero (Offensive Security Researcher) — STRONG ACCEPT
OwlC is legitimate, technically dense research that attacks a real and persistent problem — the gap between formally verified protocol designs and their inevitably buggy implementations. The combination of interaction trees for effect specification, ghost linear permission tokens for enforcement, and a cryptography-guided declassification mechanism is a genuinely novel stack, and the WireGuard case study with only 6% overhead closes the 'too slow to matter' escape hatch that kills most formal methods work.
Heather Calloway (CISO) — WEAK
Solid formal methods research with a credible proof of concept, but this talk is written for and aimed at cryptographic researchers — not defenders, operators, or security leaders. The gap between 'we verified WireGuard's core' and 'here's what your organization should do' is never crossed.
→ Top-rated talks at 34th USENIX Security Symposium (USENIX Security '25)
All talks from 34th USENIX Security Symposium (USENIX Security '25)